Armis
The Armis integration adds comprehensive device visibility and threat detection capabilities. This integration enables JupiterOne users to better manage assets, assess risks, and respond to incidents more effectively by leveraging Armis's device insights.
- Installation
- Authorization
- Data Model
- Types
- Release Notes
Installation
To install this integration, you will need to configure settings both within Armis and on JupiterOne. Before enabling in JupiterOne, ensure that you complete the setup within your Armis's account.
Configuration on Armis
You will have to configure an API secret key in Armis so that the integration can make REST API calls to fetch data from Armis.
Prerequisites
The API Secret Key must be generated by an Armis user whose role grants:
- The Generate API Secret Key permission, which allows the account to create API secret keys.
- Read access to the data types this integration ingests — at minimum Device and Vulnerability; Alerts and Sites are read with the same key.
A common approach is to duplicate the predefined Read-only role and enable Generate API Secret Key on the copy, then assign that role to the user who creates the key. When assigning the role, set the user's Allowed Sites (all sites or specific sites) to control which sites' assets the key can read.
Create the API Secret Key
-
Using a web browser, go to your Armis tenant (e.g.
https://my-tenant.armis.com) and log in with your credentials. -
If you need to create a dedicated role, go to Settings -> Roles & Permissions, duplicate the Read-only role, give it a name, and enable Generate API Secret Key. Confirm the role has read access to Device and Vulnerability data.
-
If you need a dedicated user, go to Settings -> Users -> Add User, assign the role above, and set the user's Allowed Sites.
-
Go to Settings -> API Management.
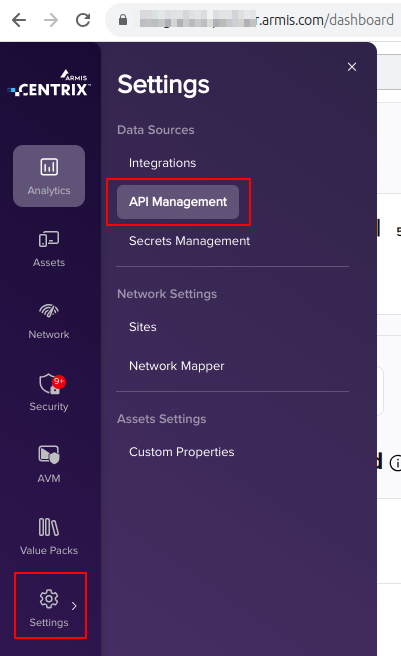
-
Click the Create button to generate a new API Secret Key.
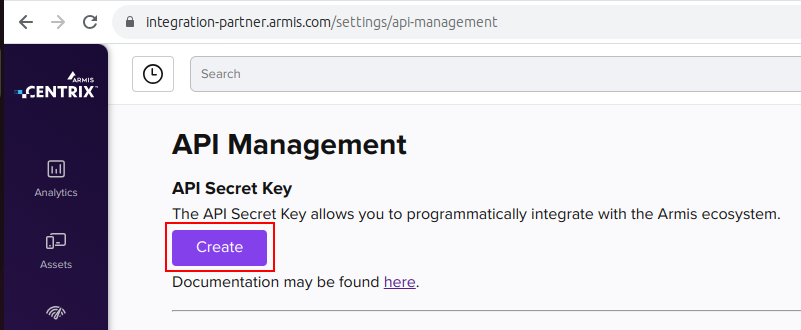
-
You will get a message box with the newly created API Secret Key. Save the key in a safe place; you will need it to configure the integration in JupiterOne.
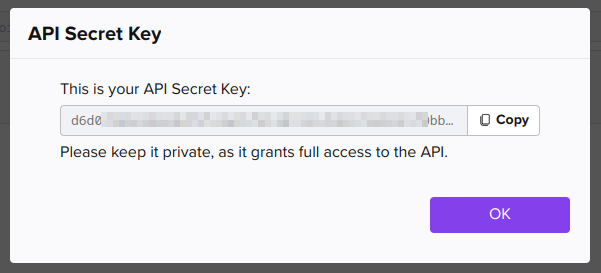
Data Volume Configuration
Control how much data is ingested from Armis to manage storage and processing.
Ingestion Windows (Time Ranges)
| Field | Description | Default | Options |
|---|---|---|---|
| Historical Days | Number of days for which data should be retrieved from Armis | 90 | Any number greater than 0 |
| Vulnerabilities Ingestion Window | Ingestion window for vulnerabilities last detected (days ago) | 90 | 90, 180, 275, 365 |
How it affects data volume: Higher number of days will result in more devices, alerts, and vulnerabilities being ingested from Armis.
Data Filtering Options
| Field | Description | Default | Options |
|---|---|---|---|
| Included Vulnerability Severities | Select which vulnerability severities to ingest | Critical, High, Medium | Critical, High, Medium, Low, Unavailable |
| Included Vulnerability Status | Select which vulnerability statuses to ingest | Open | Open, Resolved, Ignored |
How it affects data volume: Filtering by severity and status reduces the number of vulnerability entities ingested. By default, only Critical, High, and Medium severity vulnerabilities with Open status are imported.
Finalize in JupiterOne
To install the Armis integration in JupiterOne, navigate to the Integrations
tab in JupiterOne and select Armis. Click New Instance to begin configuring
the integration.
Creating an integration instance requires the following:
-
Enter the Armis URL (e.g.
https://<tenant>.armis.com) -
Enter the Armis API Secret Key generated for use by JupiterOne.
-
Enter the account name by which you want to identify this Armis account in JupiterOne.
-
[Optional] Enter a description to help your team identify the integration.
-
[Optional] Select a polling interval that is sufficient for your monitoring requirements. You can leave this as
DISABLEDand manually execute the integration. -
[Optional] Enter the Historical Days (any number greater than 0). The integration will ask Armis to return devices/alerts seen in the last few days. The Historical Days number will be used for this query. Higher number of days will result in more data ingested.
-
[Optional] Disable TLS Verification - Set this to true only if you have an on-prem Armis server that does not have a valid SSL certificate configured. For most cases this value should be false.
Click Create once all values are provided to finalize the integration.
Next steps
Now that your integration instance has been configured, it will begin running on the polling interval you provided, populating data within JupiterOne. Continue on to our Instance management guide to learn more about working with and editing integration instances.
Permissions
IAM permissions that must be granted to the integration principal for data ingestion.
Show Permissions (4)
Alerts (read)Device (read)Generate API Secret KeyVulnerability (read)
Endpoints
API endpoints that the integration makes requests to.
Show Endpoints (3)
GET /api/v1/search/GET /api/v1/sites/POST /api/v1/vulnerability-match/
Documentation Links
Links to provider documentation relevant to setup and configuration.
Show Documentation Links (2)
Per-Data-Source Breakdown
Authorization required by the steps that make up each data source. Steps that depend on a data source are listed in the Per-Step Breakdown; the complete lists are in the sections above.
Show all data sources (3)
| Data Source | Permissions | Endpoints |
|---|---|---|
| Alerts | Alerts (read), Generate API Secret Key | GET /api/v1/search/ |
| Device Vulnerabilities | Generate API Secret Key, Vulnerability (read) | POST /api/v1/vulnerability-match/ |
| Devices | Device (read), Generate API Secret Key | GET /api/v1/search/ |
Per-Step Breakdown
Detailed authorization requirements for each ingestion step.
Show all steps (2)
| Step | Permissions | Endpoints |
|---|---|---|
| Fetch Alerts | Alerts (read), Generate API Secret Key | GET /api/v1/search/ |
| Fetch Vulnerabilities | Vulnerability (read), Generate API Secret Key | POST /api/v1/vulnerability-match/ |
Entities
The following entities are created:
| Resources | Entity _type | Entity _class |
|---|---|---|
| Account | armis_account | Account |
| Alert | armis_finding_alert | Finding |
| Device | armis_device | Host |
| Site | armis_site | Site |
| Vendor | armis | Vendor |
| Vulnerability | armis_finding_vulnerability | Finding, Vulnerability |
| Vulnerability | armis_finding_vulnerability | Finding |
Relationships
The following relationships are created:
Source Entity _type | Relationship _class | Target Entity _type |
|---|---|---|
armis | HOSTS | armis_account |
armis_account | MANAGES | armis_device |
armis_account | HAS | armis_site |
armis_device | HAS | armis_finding_vulnerability |
armis_device | HAS | armis_finding_alert |
armis_site | HAS | armis_device |
Armis Device
armis_device inherits from Host
| Property | Type | Description | Specifications |
|---|---|---|---|
_key * | string | ||
ipAddress | string | ||
ipv6 | string | ||
macAddress | string |
Armis Finding Vulnerability
armis_finding_vulnerability inherits from Finding, Vulnerability
| Property | Type | Description | Specifications |
|---|---|---|---|
blocking * | boolean | null | ||
production * | boolean | null | ||
public * | boolean | null | ||
remediationActions * | string | null |
Armis Finding Vulnerability
armis_finding_vulnerability inherits from Finding
| Property | Type | Description | Specifications |
|---|---|---|---|
blocking * | boolean | null | ||
production * | boolean | null | ||
public * | boolean | null | ||
remediationActions * | string | null |
Release Notes
- 2026-04-08 — Improved OS name accuracy for Armis device entities, using human-readable OS names.
- 2025-08-19 — Added recommended actions normalization to Armis vulnerability and finding entities.
- 2025-08-05 — Added advisory ID, confidence level, remediation information, first detected, and last detected timestamps to Armis vulnerability entities.
- 2025-06-03 — Added Armis unified vulnerability ingestion, supporting both vulnerability and finding entity classes with configurable severity filtering.